Frequently Asked Questions
Why would OpenVPN connections to Zyxel USG FLEX firewalls always fail with early timeout?
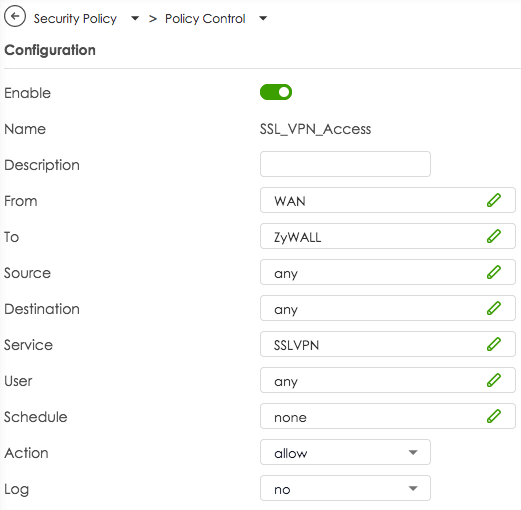
By default Zyxel creates firewall policies to allow traffic to flow from SSL VPN to LAN zone and from LAN to SSL VPN zone. Those rules are required to allow VPN traffic flow once the connection has been established. But there is no policy that actually allows VPN management traffic at the WAN port, client requests arriving at the WAN port are discarded by the firewall.
To allow an OpenVPN connection on the WAN port, you first have to create an own policy. In the main navigation, select Security Policy > Policy Control, click on the + Add button and create a policy that allows traffic for the service SSLVPN to flow from WAN to ZyWALL. Please see screenshot below.